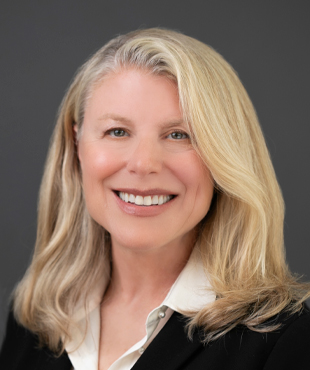
Catherine focuses her practice on cybersecurity and privacy. She advises global companies on complex cybersecurity, data governance, operational resiliency, incident response and regulatory compliance matters, helping organizations navigate business-critical risks in an increasingly complex and evolving digital environment. Her practice spans proactive risk management, cybersecurity preparedness, internal investigations and crisis response, with a focus on protecting clients’ legal, technical, operational and reputational interests.
Catherine has extensive experience guiding organizations through significant cybersecurity incidents, including destructive malware attacks, zero-day vulnerabilities, data compromise events and sensitive internal investigations. Working alongside executive leadership teams, she helps clients make strategic decisions during high-stakes events while managing regulatory scrutiny, stakeholder communications and business continuity challenges.
Catherine also counsels clients on information and data governance, third-party and supplier risk, secure development and evolving data protection requirements.
Before returning to private practice, Catherine served as senior counsel at a major telecommunications company, where she advised on information governance, data and discovery strategies, and technology and operational matters.
Representative Matters
Advised a global software security company in connection with an FTC investigation arising from a zero-day vulnerability, including investigation and regulatory response strategy. The matter was closed without further action.
Led review and response strategy for a global automotive manufacturer in connection with an FTC inquiry concerning a publicly reported cybersecurity and privacy vulnerability, including preparing senior cybersecurity executives for engagement with the agency. The matter was closed without further action.
Led the investigation and response for a financial services company following a significant cybersecurity incident, including preparation for engagement with federal financial regulators. The matter was closed without further action.
Advised multi-national organizations in connection with significant cybersecurity incidents, including destructive malware, zero-day vulnerabilities, and other operationally disruptive events, coordinating legal, forensic, security, regulatory and communication workstreams.
Developed incident response, regulatory disclosure and crisis communication frameworks for global organizations, including programs addressing the NYDFS Cybersecurity Regulation.
Advised a leading pharmaceutical company in implementation of the U.S. Department of Justice Data Security Program, including governance, documentation and operational processes addressing access to sensitive U.S. data.
Advised a global medical technology company on cybersecurity and privacy risks associated with a strategic acquisition, including diligence, risk assessment and integration considerations.
Advised an automotive company on secure software and application development, supplier security, connected vehicle cybersecurity and technology risks involving foreign telecommunications providers.
Advised a U.S. subsidiary of a global communications technology provider on sensitive internal governance involving U.S. Department of Defense contracting requirements and related regulatory, operational and reputational considerations.
Advised a global hospitality company in connection with a state attorney general investigation following a data breach, including regulatory response and remediation strategy.